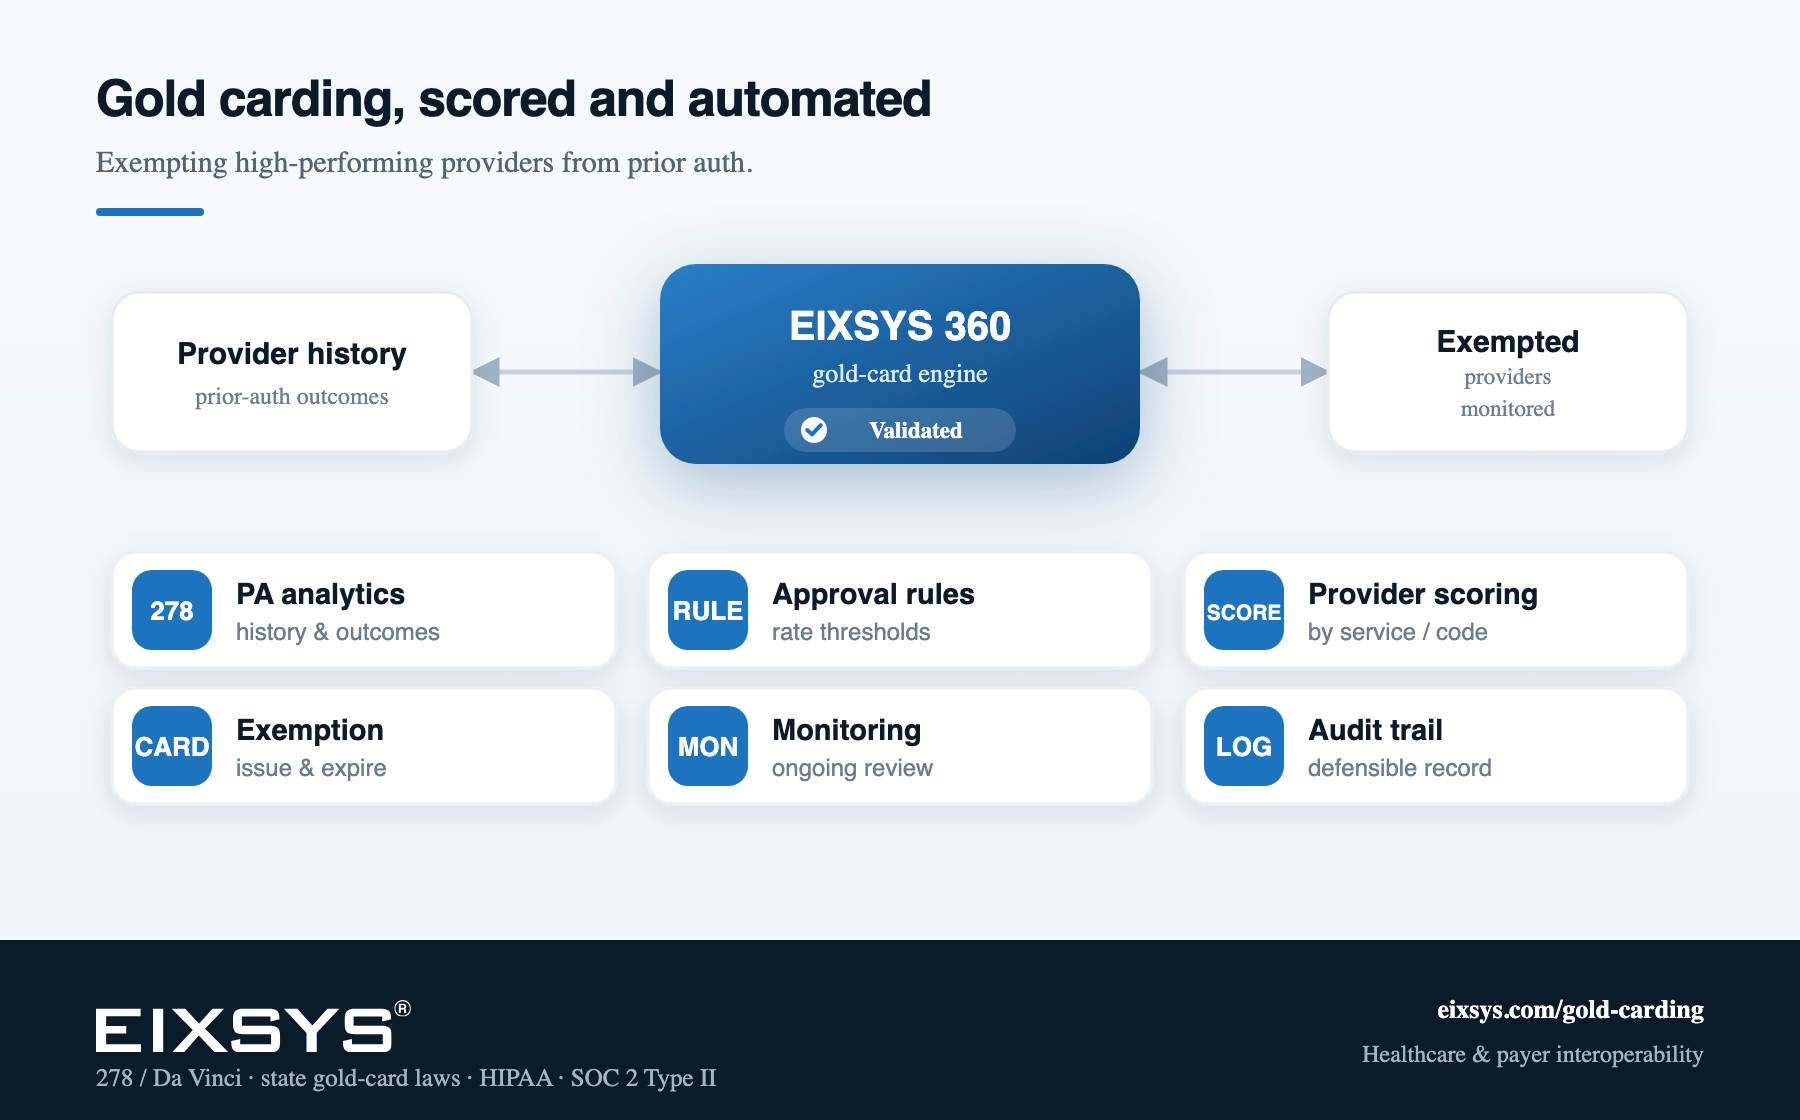
We help plans run defensible gold-carding programs — analyzing prior-authorization history, scoring providers against your rules, issuing exemptions and monitoring them — so low-value prior auth goes away without losing control.
Gold carding is increasingly required by state law and expected by providers, but doing it well is a data problem. You have to measure each provider’s prior-authorization approval rate by service accurately, apply consistent rules, issue and expire exemptions, and prove the whole thing was fair if challenged. Done by hand it’s slow and hard to defend; done without rigor it creates risk.
Accurate measurement of prior-authorization volume and outcomes by provider and service, the evidence a program stands on.
Your qualification thresholds encoded consistently — so a provider earns a gold card by the same rule every time.
Scoring by provider and procedure, so exemptions are targeted to where the data supports them.
Issue, communicate and expire gold-card exemptions on schedule, wired into your prior-auth workflow.
Continuous review so a provider whose performance changes is re-evaluated, not exempt forever by default.
A defensible record of how every exemption was earned and reviewed — for regulators, providers and your own compliance team.
Built on the 278 and Da Vinci prior-authorization standards, applicable state gold-card laws, HIPAA, SOC 2 Type II and PCI DSS.
Less low-value prior authorization, happier high-performing providers, and a program that meets state requirements with an audit trail you can defend — without giving up oversight.
Gold carding exempts providers with consistently high prior-authorization approval rates from having to request prior auth for certain services — reducing administrative burden for providers who have earned the plan’s trust. A number of states now mandate it.
By measuring each provider’s prior-authorization approval rate by service against the rules you set, consistently and with an audit trail — so qualification is defensible.
The 278 transaction and the CMS-0057-F Prior Authorization API carry prior-auth requests electronically. Gold carding sits on top — it decides when a provider doesn’t need to send one at all.